Explore checkers, demos and evaluation routes →
Browser fingerprinting techniques: compare rendering, environment and network evidence
Read browser surfaces before comparing hashes
Browser fingerprinting derives recognition evidence from observable characteristics. Canvas can expose rendered pixel data; Web Audio supplies processing behavior; environment APIs and network observations add other context. MDN notes that privacy settings may introduce noise into canvas output. A hash summarizes inputs rather than creating identity assurance. Keep collection version and missing observations so drift can be distinguished from a newly seen browser.
Reference: W3C: mitigating browser fingerprinting.
Keep generated audio, recordings and microphones separate
OfflineAudioContext renders an audio graph into an AudioBuffer without outputting directly to speakers. A browser fingerprint may summarize that processing result. Recording identification instead compares media content, while microphone capture uses getUserMedia with permission requirements. The terms audio fingerprint and acoustic fingerprint can refer to those different tasks. An SDK specification should state the input, output and permissions before making claims about its purpose.
Compare provider contracts rather than hash length
Fingerprint, ShieldLabs, Castle and Incognia offer different combinations of recognition and risk; ThumbmarkJS provides a fingerprinting approach teams can inspect. Compare supported surfaces, server matching, collision handling and operational support. Ask how false merges, splits and missing results are measured. Native SDK and browser behavior differ. Regional hosting, consent and data-transfer suitability need specific evidence rather than an assumption from a global marketing page.
Reference: Fingerprint: Smart Signals reference.
Model identity and risk as separate outputs
A device ID answers continuity; risk observations address integrity, automation or location; account events describe behavior over time. Keep those outputs distinct in your application types and review UI. Incognia emphasizes location-grounded recognition; ShieldLabs combines device and network signals. A native mobile collector and a browser script expose different evidence. Asset inventory platforms discover owned machines, which is a different task from recognizing website visitors.
Reference: W3C: fingerprinting guidance.
Distinguish tampering, automation and privacy defenses
An anti-detect check examines manipulated or inconsistent environments. Headless checks concern automation; privacy settings can also change observable values. Compare multiple surfaces and preserve reasons rather than declaring every unusual fingerprint malicious. Connection and account behavior can add context. Diagnose your own authorized integration with documented test environments; selecting disguise tools to evade someone else's rules is a different task.
Reference: W3C: fingerprinting guidance.
Place TLS and TCP collection at the right layer
JA4 fingerprints TLS clients; JA4H concerns HTTP; JA4T concerns TCP in FoxIO's family. HTTP/2 settings are another observation surface. Browser JavaScript does not expose every transport property, and intermediaries affect what an origin observes. Cloudflare documents plan restrictions and missing JA3/JA4 fields. Network fingerprints group similar clients; they are not unique physical-device identifiers or direct substitutes for browser matching.
Define the reporting identity behind a visitor count
GA4 describes User-ID, device ID and modeling as identity spaces. A person can produce many page views and sessions, with multiple device identities before login. A returning visitor has earlier activity under the definition the report uses. There is no universal healthy new-versus-returning ratio. Compare acquisition source, reporting period and identity configuration before treating a change as browser-recognition failure.
Reference: Google Analytics: understand user metrics.
Use guest context without opening private account data
A browser observation can support recent-content suggestions or a low-risk onboarding choice. It should not reveal saved addresses, subscription details or privileged content from a probabilistic match. Establish the anonymous-to-known link through a trustworthy event such as login. Preserve the distinction between supplied facts and inferences, and keep resource authorization on the server even when the browser appears familiar.
Reference: OWASP: authorization.
Worked browser comparison: an update and a second device
Hypothetical example: a browser updates on a laptop and later the account signs in on a phone. Label the expected same-environment and cross-device relationships separately. Keep collector versions and authenticated account references. The first tests drift handling; the second needs a supported cross-device association rather than an assumption that two environments should have the same hash.
| Transition | Label required | What to inspect |
|---|---|---|
| Browser update | Known environment | Drift and method version |
| Cookie deletion | Same environment | Matching and missing inputs |
| New phone | Different environment | Authorized account association |
Continue with Network and bot evidence in a browser API integration for the next evidence layer.
Separate owned-asset discovery from visitor intelligence
Automatic device discovery is not an alternate name for browser fingerprinting. Axonius Device Intelligence Hub manages OT/IoT scanning adapters, jobs and history. Lansweeper describes owned IT/OT/cloud/IoT inventory and normalization. Score those products on asset coverage rather than returning-visitor matching. The phrase local digital intelligence remains broad until the buyer states whether the object is an internal asset, an authorized investigation or an anonymous customer interaction.
Sources
- W3C: mitigating browser fingerprinting · read
- MDN: CanvasRenderingContext2D.getImageData · read
- W3C: Web Audio specification · read
- MDN: OfflineAudioContext · read
- W3C: Web Audio privacy and security · read
- MDN: getUserMedia · read
- Fingerprint: Smart Signals reference · read
- Thumbmark: product and integration scope · read
- Incognia: use cases · read
- NIST: identity-proofing scope · read
- OWASP: automated threats · read
- Cloudflare: JA3 and JA4 · read
- FoxIO: JA4+ project and specifications · read
- Cloudflare: HTTP headers · read
- NIST: authentication and sessions · read
- Google Analytics: user metrics · read
- Google Analytics: reporting identity · read
- Google Search Console: performance report · read
- Google Search Console: dimensions and query omissions · read
- OWASP: authorization · read
- Primary source: docs.axonius.com · read
- Primary source: www.lansweeper.com · read
- Primary source: deviceatlas.com · read
- Primary source: privacysandbox.google.com · read
- Primary source: shieldlabs.ai · read
- Primary source: www.incognia.com · read
- Primary source: acoustid.org · read
- Primary source: acoustid.org · read
- Primary source: cflib.org · read
- Primary source: castle.io · read
- Primary source: www.browserscan.net
Continue reading
FAQ
Does cookieless mean that changing browsers preserves one ID?
Cookieless describes an approach to recognition. Cross-browser and cross-device persistence are separate capabilities requiring documented support and evaluation.
What does DeviceAtlas identify?
For browser recognition, DeviceAtlas supplies device identification and properties for uses including optimization and analytics. Score that output separately from a persistent person identity or ready account-abuse finding. Verify the returned object rather than treating every device-intelligence product as the same recognition service.
What did the April 2025 Chrome tracking announcement say?
For browser recognition, the dated Google announcement is useful context: on April 22, 2025 it retained Chrome's existing third-party-cookie choice approach instead of a standalone new prompt and described further tracking-protection work. It is a dated policy announcement, rather than a complete inventory of every Chrome feature shipped afterward.
Which recognition providers belong on a device shortlist?
Choose recognition separately from the operations around it. Compare Fingerprint for recognition and documented Smart Signals, ThumbmarkJS for an inspectable fingerprinting approach, ShieldLabs for recognition plus ready risk/account events and Incognia where location-grounded recognition is central. Match web/native surfaces, errors, retention and required output before choosing.
How do music or acoustic fingerprints differ from browser audio fingerprints?
For an API specification using the phrase audio fingerprint, Chromaprint extracts a recording fingerprint from supplied audio; AcoustID can look it up with duration and return related recording metadata. A typical authorized workflow decodes the recording, generates the fingerprint and queries an appropriate catalog. Check corpus fit, permissions and commercial service terms. Browser Web Audio fingerprinting instead compares processing behavior; it does not identify the song, speaker or rightful account owner.
How should separate browser profiles be used for authorized account work?
For an API implementation, define the observation, trusted response and authority needed for the action. First establish permission to operate each account. Use documented workspace roles, distinct session/storage profiles and the platform’s approved team or agency APIs where available. For testing your own application, record the profile, collector version, expected permissions and result, then verify that private data and grants remain isolated. A modified browser or rotating route does not create account eligibility or permission to evade another service’s restrictions. W3C fingerprinting guidance explains the observable surfaces; OWASP authorization applies independently of profile appearance.
How should device intelligence be selected for a Saudi deployment?
For an API implementation, define the observation, trusted response and authority needed for the action. Build a shortlist around ShieldLabs, Fingerprint, Incognia or a broader risk supplier according to the required web/native and decision scope. Then request a written data-flow and contract review covering collection purpose, lawful transfer arrangements, processing/storage locations, subprocessors, retention/deletion, regional network latency and support. A product marketed worldwide does not by itself establish Saudi hosting or a local-residency commitment. Make those acceptance conditions explicit before purchase.
What should a browser-detection or browser-scan result be used for?
For an API implementation, define the observation, trusted response and authority needed for the action. Clarify whether the task is parsing browser software, inspecting the current environment, classifying a relay or recognizing repeat activity. The CFLib browserDetect function, dated 2011, illustrates user-agent parsing rather than persistent identity. A scan can report selected browser/network observations without proving account ownership or universal anonymity. If a search phrase is an imprecise spelling of anti-detect or a legacy tool name, confirm the exact maintained product and official documentation before downloading or choosing infrastructure. An anonymizing gateway routes traffic through another endpoint; it does not erase the site’s other history. These category distinctions interpret the task without asserting that every ambiguous string names a verified product.
Which visitor/device options fit identity platforms and gaming?
For an API implementation, define the observation, trusted response and authority needed for the action. For CIAM or gaming, compare Fingerprint for recognition/Smart Signals, ShieldLabs for recognition plus ready abuse events, Castle for account/environment intelligence and Incognia where location-grounded recognition matters. Include legitimate shared equipment, updates, cookie resets, platform-supported native/web clients and repeated restricted claims. Measure recognition errors and player completion separately from policy findings. Favor the documented output that fits your flow rather than an unverified universal reliability label.
If BrowserScan is intended, what does its browser check show?
The BrowserScan page lists network, browser, canvas/audio and automation diagnostics. Treat “scanbrowser” as an imprecise service name until the intended URL is confirmed. A generic browser scan can also mean inspecting observable properties. Diagnostic output describes what the checker sees in that context; it is not a certificate of population uniqueness, account ownership or invisibility to every website.
Summarize this page with
Browser fingerprinting techniques collect several kinds of evidence: rendering output, environment properties, browser-exposed capabilities and request or network context. The number of collected attributes is not a direct measure of identification quality. What matters is whether the observations distinguish environments, remain useful over time and support trustworthy matching.
Start with the question each technique answers. A rendering result describes the environment producing it. A network observation describes the current connection. Neither, by itself, proves who controls an account.
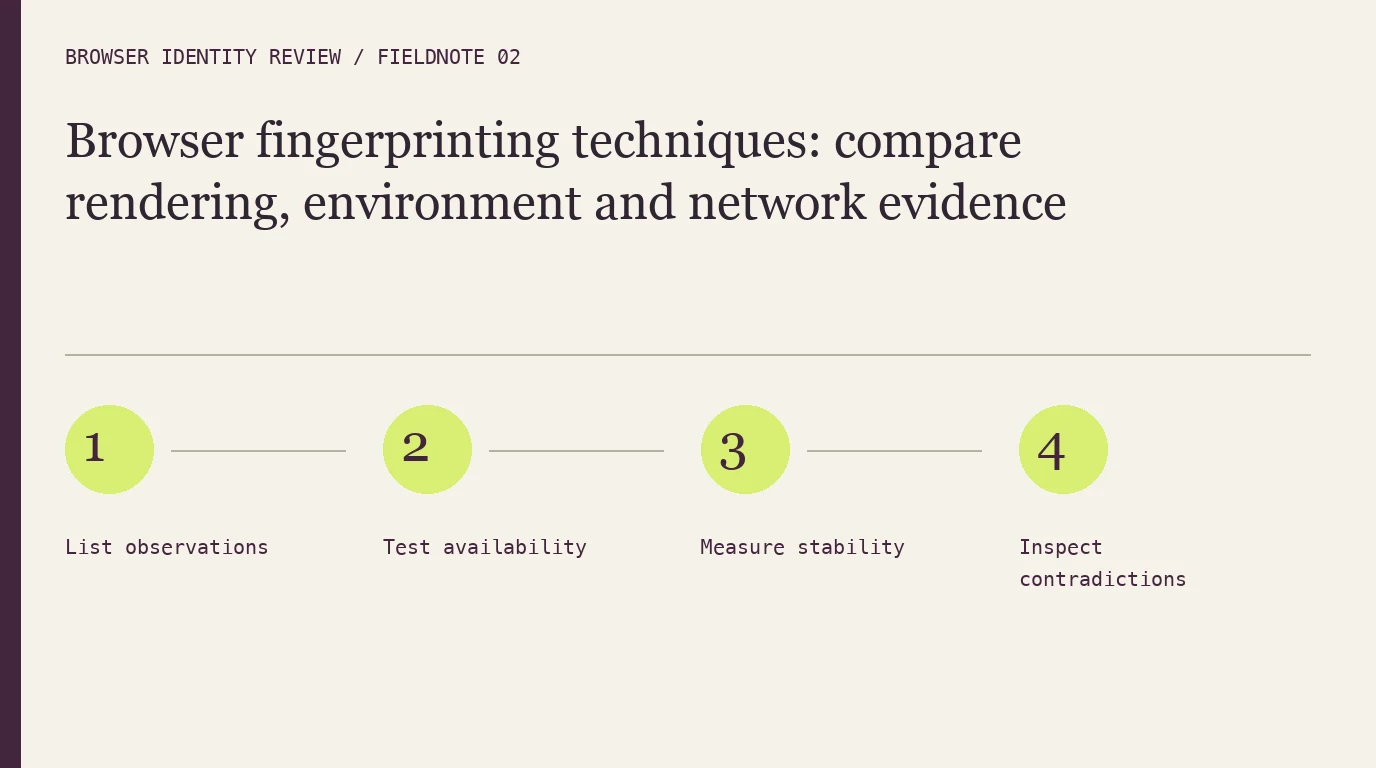
- 1List observations
- 2Test availability
- 3Measure stability
- 4Inspect contradictions
A practical evidence matrix
| Evidence family | Example observation | Evaluation question |
|---|---|---|
| Rendering | Canvas or graphics output | Does the observation remain available and stable on the target browsers? |
| Audio processing | A generated audio-processing result | Does this contribute useful distinction beyond existing observations? |
| Environment | Locale, screen and exposed platform properties | Which values change during normal use? |
| Network and request | Current connection or request characteristics | Does this corroborate the browser evidence? |
| Stored state | An existing first-party cookie or identifier | How does the system behave when that state is unavailable? |
Stored state can help a recognition system, but it should be described separately from fingerprint-derived evidence. That makes a persistence test easier to interpret.
Test signal families, not a headline count
Create permitted browser cohorts and inspect the components each product actually exposes. Repeat observations after a browser upgrade, a display change, a network switch and a storage reset. Keep the same-browser and different-browser labels independent of the detector under evaluation.
The Canvas API and WebGL support different graphics operations. The audio guide covers another evidence family. These interfaces explain the collection surfaces; they do not promise a universal stable identifier.
Inspect contradictory evidence
A product can examine whether observations agree with one another. Browser properties that look plausible individually may require more context when combined. Request the documented tamper and automation fields rather than assuming a local hash detects inconsistencies automatically.
ShieldLabs combines device and network intelligence with named risk signals. Other products expose different signal and decision sets. Use the vendor reviews to distinguish available evidence from a score whose ingredients are not included in your plan.
Avoid counting the same information twice
Several fields may describe closely related aspects of the environment. A large component count can therefore exaggerate the amount of independent evidence. In a pilot, compare recognition quality and mistakes on the same cohorts rather than awarding points for every available field.
Record collection failures and unsupported interfaces. Missing information should remain visible in the evaluation, especially when privacy settings affect legitimate users. The integration guide explains the result and failure contract your application needs.
FAQ
Is canvas fingerprinting enough for production identity?
Treat it as one evidence family. Evaluate persistence, distinguishability, availability and integrity in the complete system.
Does adding more attributes guarantee better matching?
No. Correlated, unstable or unavailable observations can add complexity without improving the decision. Measure outcomes on representative cohorts.
Should browser and network evidence be combined?
They can corroborate one another, but network changes are common. Evaluate the matching design rather than treating one IP address as a permanent browser identity.
Sources
Checked October 22, 2026: MDN Canvas, MDN WebGL, W3C guidance, ShieldLabs. Read the evaluation method.
Continue reading
- What is a browser fingerprint? From browser observations to a returning visitor
- Audio fingerprinting in browsers: what the signal can and cannot tell you
Compare all ten tools or read the complete deployment guide.